公开接口档案
为 AI Agent 提供结构化、可追溯的金融事实。
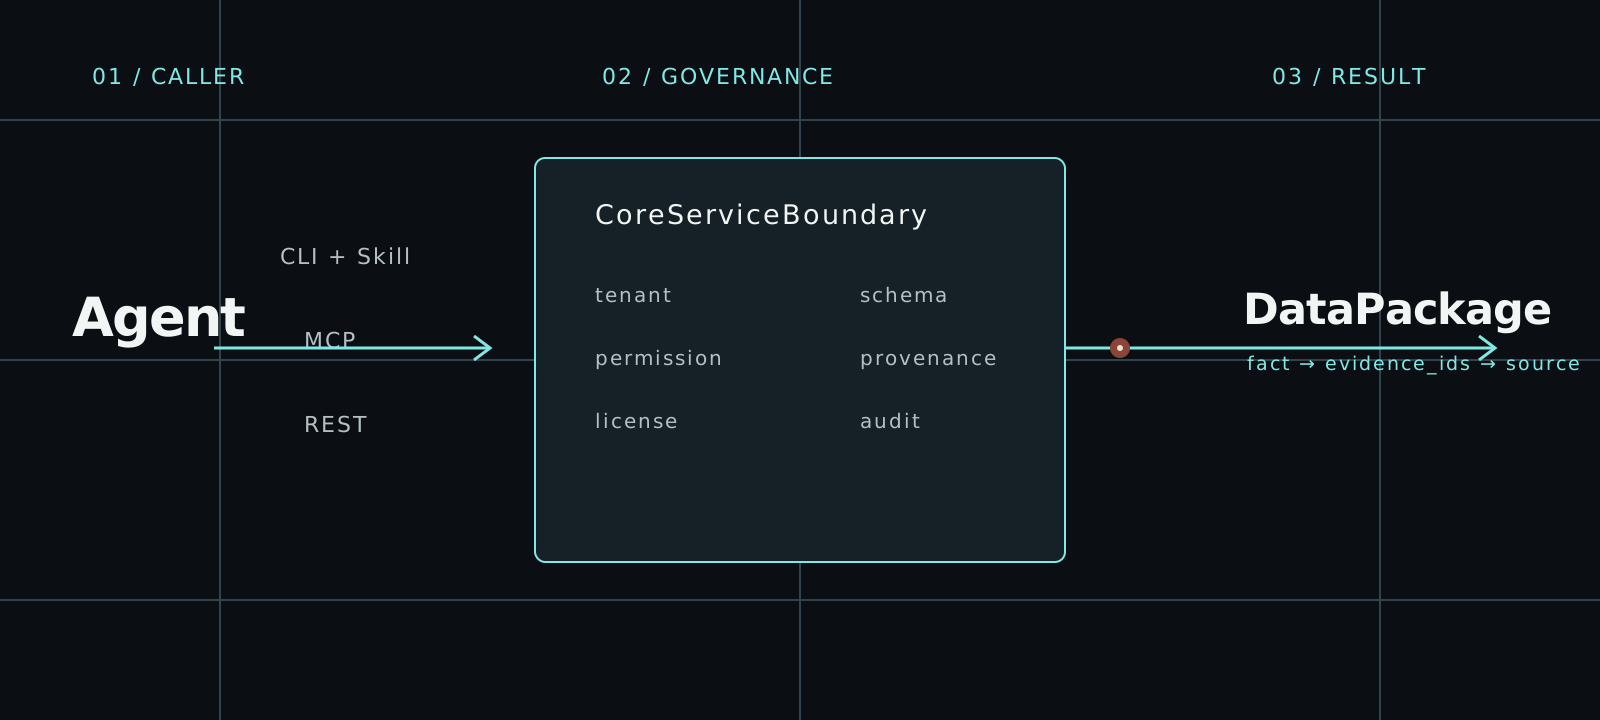
CLI + Skill 和 MCP 是主要的 Agent 接口;REST 提供 HTTPS 和批量传输。 每个响应都包含状态和治理元数据;返回的事实关联来源证据和时间语义。
选择适合你的 AI agent 的接口
三种访问路径均进入同一个 CoreServiceBoundary。Tenant、权限、许可证、证据、溯源和审计规则不会因客户端而改变。
01CLI
argus auth login
argus --base-url https://api.argusfa.com entity-resolve \
  --identifier-type lei \
--identifier-value HWUPKR0MPOU8FGXBT39402REST
# First run: argus auth login
import json
from urllib.request import Request, HTTPRedirectHandler, build_opener
from argus.cli.oauth import CliOAuthProfile

profile = CliOAuthProfile()
token = profile.client().access_token()
if token is None:
    raise RuntimeError("Run argus auth login first")

class NoRedirect(HTTPRedirectHandler):
    def redirect_request(self, *args, **kwargs):
        return None

request = Request(
    profile.api_base_url + "/v1/entity-resolve",
    data=json.dumps(json.loads(r'''{"identifier_type":"lei","identifier_value":"HWUPKR0MPOU8FGXBT394","purpose":"factual_lookup","requires_redistribution":false}''')).encode(),
    headers={"Authorization": f"Bearer {token}",
             "Content-Type": "application/json", "User-Agent": "Argus REST client"},
    method="POST",
)
with build_opener(NoRedirect()).open(request, timeout=30) as response:
    envelope = json.load(response)
print(json.dumps(envelope, indent=2))03MCP
# 仅需安装一次: use the official Argus installer.
# argus auth login --interface mcp
import asyncio
import json
from datetime import timedelta

from argus.cli.oauth import CliOAuthProfile
from mcp import ClientSession
from mcp.client.streamable_http import streamable_http_client
from mcp.shared._httpx_utils import create_mcp_http_client


def decode_tool_result(response):
    if response.isError:
        raise RuntimeError(response.content)
    if response.structuredContent is not None:
        return response.structuredContent
    text = next(block.text for block in response.content if block.type == "text")
    return json.loads(text)


async def main() -> None:
    tool_name = "entity_resolve"
    arguments = json.loads(r'''{"identifier_type":"lei","identifier_value":"HWUPKR0MPOU8FGXBT394","purpose":"factual_lookup","requires_redistribution":false}''')
    profile = CliOAuthProfile.from_environment().for_interface("mcp")
    token = profile.client().access_token()
    if token is None:
        raise RuntimeError("Run argus auth login --interface mcp first")

    async with (
        create_mcp_http_client(headers={"Authorization": f"Bearer {token}"}) as http,
        streamable_http_client(profile.audience, http_client=http) as (read, write, _),
    ):
        async with ClientSession(
            read,
            write,
            read_timeout_seconds=timedelta(seconds=30),
        ) as session:
            await session.initialize()
            listed_tools = {tool.name for tool in (await session.list_tools()).tools}
            registry = decode_tool_result(
                await session.call_tool("agent_tool_registry")
            )
            registry_tools = {tool["tool_name"] for tool in registry["tools"]}
            if tool_name not in listed_tools or tool_name not in registry_tools:
                raise RuntimeError(f"当前工具注册表中没有此工具: {tool_name}")

            response = await session.call_tool(
                tool_name,
                arguments=arguments,
            )
            payload = decode_tool_result(response)
            if payload.get("success") is not True:
                error = payload.get("error")
                audit_id = payload.get("audit_id")
                if audit_id is None and isinstance(error, dict):
                    audit_id = error.get("audit_id")
                raise RuntimeError(f"Argus 请求失败 (audit_id={audit_id}): {error}")
            print(json.dumps(payload, indent=2, ensure_ascii=False))


asyncio.run(main())一条完整的受治理调用路径
先发现,后执行。无论成功还是拒绝,每次调用都保持结构化、有边界且可审计。
- 01
identityOAuth subject · scopes · purpose · as_of - 02
registryagent_tool_registry · scopes · allowed_purposes - 03
boundarytenant · permission · license · provenance · audit - 04
DataPackagefacts · source_evidence · known_time · quality · audit_id
可复用的请求参考
调用工具前,请先通过 OAuth 登录。这些请求使用真实的 GLEIF 法律实体;使用结果前,请检查返回的覆盖范围和证据。请将无人值守机器使用的凭据保存在你的机密环境中。
- 通过交互式 OAuth 连接 AI agent;无人值守自动化使用 machine client 或 service account。
- 先读取工具注册表,选择权限范围和用途与身份匹配的工具。
- 使用 CLI + Skill 或 MCP 作为主要的 Agent 接口;使用 REST 进行 HTTPS 和批量传输。
- 调用时明确提供 as_of 时间。
- 使用事实前检查证据、质量、许可、限制和 audit_id。
验证数据包,而不只检查状态码
传输成功并不代表事实可直接使用。进入下游自动化前,应检查受治理响应封装和其中的 DataPackage。
这里只展示请求语法。请使用真实标识符、先前调用返回的证据,以及覆盖情况已确认的时间范围。此示例不代表已完成的生产业务结果。
{
  "success": true,
  "tool_name": "company_fact_snapshot",
  "output_format": "json",
  "audit_id": "audit_01JYEXAMPLE0000000000000000",
  "data_package_version": "company-fact-snapshot-cli-v1",
  "source_evidence": [
    {
      "evidence_id": "evidence:filing:1",
      "source_type": "regulatory_filing",
      "source_file_id": "filing:example-inc:2025-10k",
      "document_url": "https://regulator.example.test/filings/example-inc-2025-10k",
      "fragment_position": "char:1024-1080",
      "page_number": 42,
      "paragraph_position": null,
      "field_path": "filing.financials.revenue",
      "filing_time": "2026-06-15T09:00:00Z",
      "retrieved_at": "2026-06-16T09:30:00Z",
      "parser_version": "filing-parser-v1",
      "evidence_confidence": 0.99,
      "credibility_level": "regulatory_original",
      "pointer_type": "source_fragment",
      "content_trust": "untrusted_source_text",
      "mime_type": "text/plain",
      "source_object_sha256": null,
      "excerpt_boundary": "external_source_data",
      "is_conflicting": false,
      "conflict_group_id": null
    }
  ],
  "permission_result": {
    "allowed": true,
    "checked_at": "2026-06-16T10:00:00Z",
    "missing_permissions": [],
    "reason": "permission_allowed",
    "safe_alternative_tools": [
      "company_fact_snapshot",
      "filing_search",
      "source_evidence_lookup"
    ]
  },
  "license_status": "authorized",
  "output_restrictions": [
    "machine_readable_json",
    "cite_source_evidence"
  ],
  "result": {
    "package_type": "company_fact_snapshot",
    "package_version": "company-fact-snapshot-cli-v1",
    "generated_at": "2026-06-16T10:00:00Z",
    "request_subject": "company:example-inc",
    "caller_id": "service:customer-agent",
    "institution_id": "institution:customer",
    "request_purpose": "factual_lookup",
    "facts": [
      {
        "fact_id": "fact:revenue",
        "fact_type": "financial_metric",
        "field_name": "revenue",
        "value": 125000000,
        "evidence_ids": [
          "evidence:filing:1"
        ],
        "credibility_level": "regulatory_original",
        "extraction_method": "structured_source",
        "confidence": 0.99,
        "review_status": null
      }
    ],
    "sections": [],
    "source_evidence": [
      {
        "evidence_id": "evidence:filing:1",
        "source_type": "regulatory_filing",
        "source_file_id": "filing:example-inc:2025-10k",
        "document_url": "https://regulator.example.test/filings/example-inc-2025-10k",
        "fragment_position": "char:1024-1080",
        "page_number": 42,
        "paragraph_position": null,
        "field_path": "filing.financials.revenue",
        "filing_time": "2026-06-15T09:00:00Z",
        "retrieved_at": "2026-06-16T09:30:00Z",
        "parser_version": "filing-parser-v1",
        "evidence_confidence": 0.99,
        "credibility_level": "regulatory_original",
        "pointer_type": "source_fragment",
        "content_trust": "untrusted_source_text",
        "mime_type": "text/plain",
        "source_object_sha256": null,
        "excerpt_boundary": "external_source_data",
        "is_conflicting": false,
        "conflict_group_id": null
      }
    ],
    "data_period": {
      "start": "2025-01-01T00:00:00Z",
      "end": "2025-12-31T23:59:59Z"
    },
    "filing_time": "2026-06-15T09:00:00Z",
    "known_time": "2026-06-16T09:30:00Z",
    "revision_time": null,
    "invocation_time": "2026-06-16T10:00:00Z",
    "data_quality": {
      "quality_level": "high",
      "issues": [],
      "requires_human_review": false
    },
    "credibility_level": "regulatory_original",
    "data_license": {
      "license_id": "public-disclosure-v1",
      "source": "regulatory_filing",
      "status": "authorized",
      "allowed_uses": [
        "factual_lookup",
        "audit_reproduction"
      ],
      "prohibited_uses": [
        "restricted_redistribution"
      ],
      "redistribution": "restricted",
      "authorized_institutions": [
        "institution:customer"
      ],
      "restricted_fields": []
    },
    "allowed_uses": [
      "factual_lookup",
      "audit_reproduction"
    ],
    "prohibited_uses": [
      "restricted_redistribution"
    ],
    "output_restrictions": [
      "machine_readable_json",
      "cite_source_evidence"
    ],
    "structured_output_flags": {},
    "audit_id": "audit_01JYEXAMPLE0000000000000000",
    "output_policy_version": "[email protected]"
  }
}工具
公开工具注册表当前定义了 53 个受治理工具。以下代表性记录与工具目录使用同一份权威构建数据生成。
- 01
- REST
/v1/company-fact-snapshot- MCP
company_fact_snapshot- 返回契约
- CliToolEnvelope JSON with nested DataPackage result
- 02
- REST
/v1/point-in-time-snapshot- MCP
point_in_time_snapshot- 返回契约
- CliToolEnvelope JSON with nested DataPackage result
- 03
- REST
/v1/evidence-gap-report- MCP
evidence_gap_report- 返回契约
- CliToolEnvelope JSON with nested DataPackage result
- 04
- REST
/v1/agent-data-preflight- MCP
agent_data_preflight- 返回契约
- CliToolEnvelope JSON with nested agent_data_preflight_result DataPackage
信任
Argus 提供边界清晰的事实基础设施。拒绝、限制、新鲜度、许可状态和人工复核要求都会保留在结果中。
[POLICY]Argus 自身不生成投资判断或执行订单,但不限制客户端 AI Agent 使用合法取得的数据独立推理和输出。
继续阅读权威接入指南
从首次请求指南开始,检查全部工具,或直接进入你的 AI agent 所用的接口文档。